WebMap: Improper Neutralization of Special Elements used in a Command
CVE-2026-90843 is a high-severity improper neutralization of special elements used in a command vulnerability in WebMap from SabyasachiRana, with a CVSS 3.1 base score of 8.3 out of 10. It can be exploited remotely over the network by an unauthenticated attacker, without any action from a user. Affected WebMap versions: 8b95fe4dc301a3c09ddf145b895de0bf9f8d2a25. The record does not name a fixed version, so check the vendor advisory. There is no confirmed exploitation so far. EPSS estimates a 2.18% chance of exploitation within 30 days, higher than 83% of scored CVEs.
High severity with no evidence of exploitation so far.
What to do
- Check which version of WebMap you run against the affected versions below, and install the vendor's latest release.
- Until you can update, restrict network access to the affected service so it is not reachable from untrusted networks.
Affected products and versions
| Vendor | Product | Affected versions | Fixed in |
|---|---|---|---|
| SabyasachiRana | WebMap | 8b95fe4dc301a3c09ddf145b895de0bf9f8d2a25 | Not stated |
Version data comes from the organisation that assigned the CVE. Confirm against the vendor advisory before deciding you are unaffected.
How the severity score breaks down
- Attack vector
- NetworkCan be exploited remotely over a network, including the internet.
- Attack complexity
- LowNo special conditions are needed; the attack works reliably.
- Privileges required
- NoneNo account or login is needed.
- User interaction
- NoneNo action by a victim is required.
- Scope
- ChangedThe attack can reach beyond the vulnerable component into other systems.
- Confidentiality
- LowSome restricted data can be read.
- Integrity
- LowLimited modification of data is possible.
- Availability
- LowPerformance or availability is reduced.
Vector: CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:C/C:L/I:L/A:L. Scored by CNA (vuldb.com).
| Scoring system | Score | Severity | Scored by |
|---|---|---|---|
| CVSS 4.0 | 5.5 | Medium | CNA (vuldb.com) |
| CVSS 3.1 | 8.3 | High | CNA (vuldb.com) |
| CVSS 2.0 | 7.5 | High | CNA (vuldb.com) |
Official description
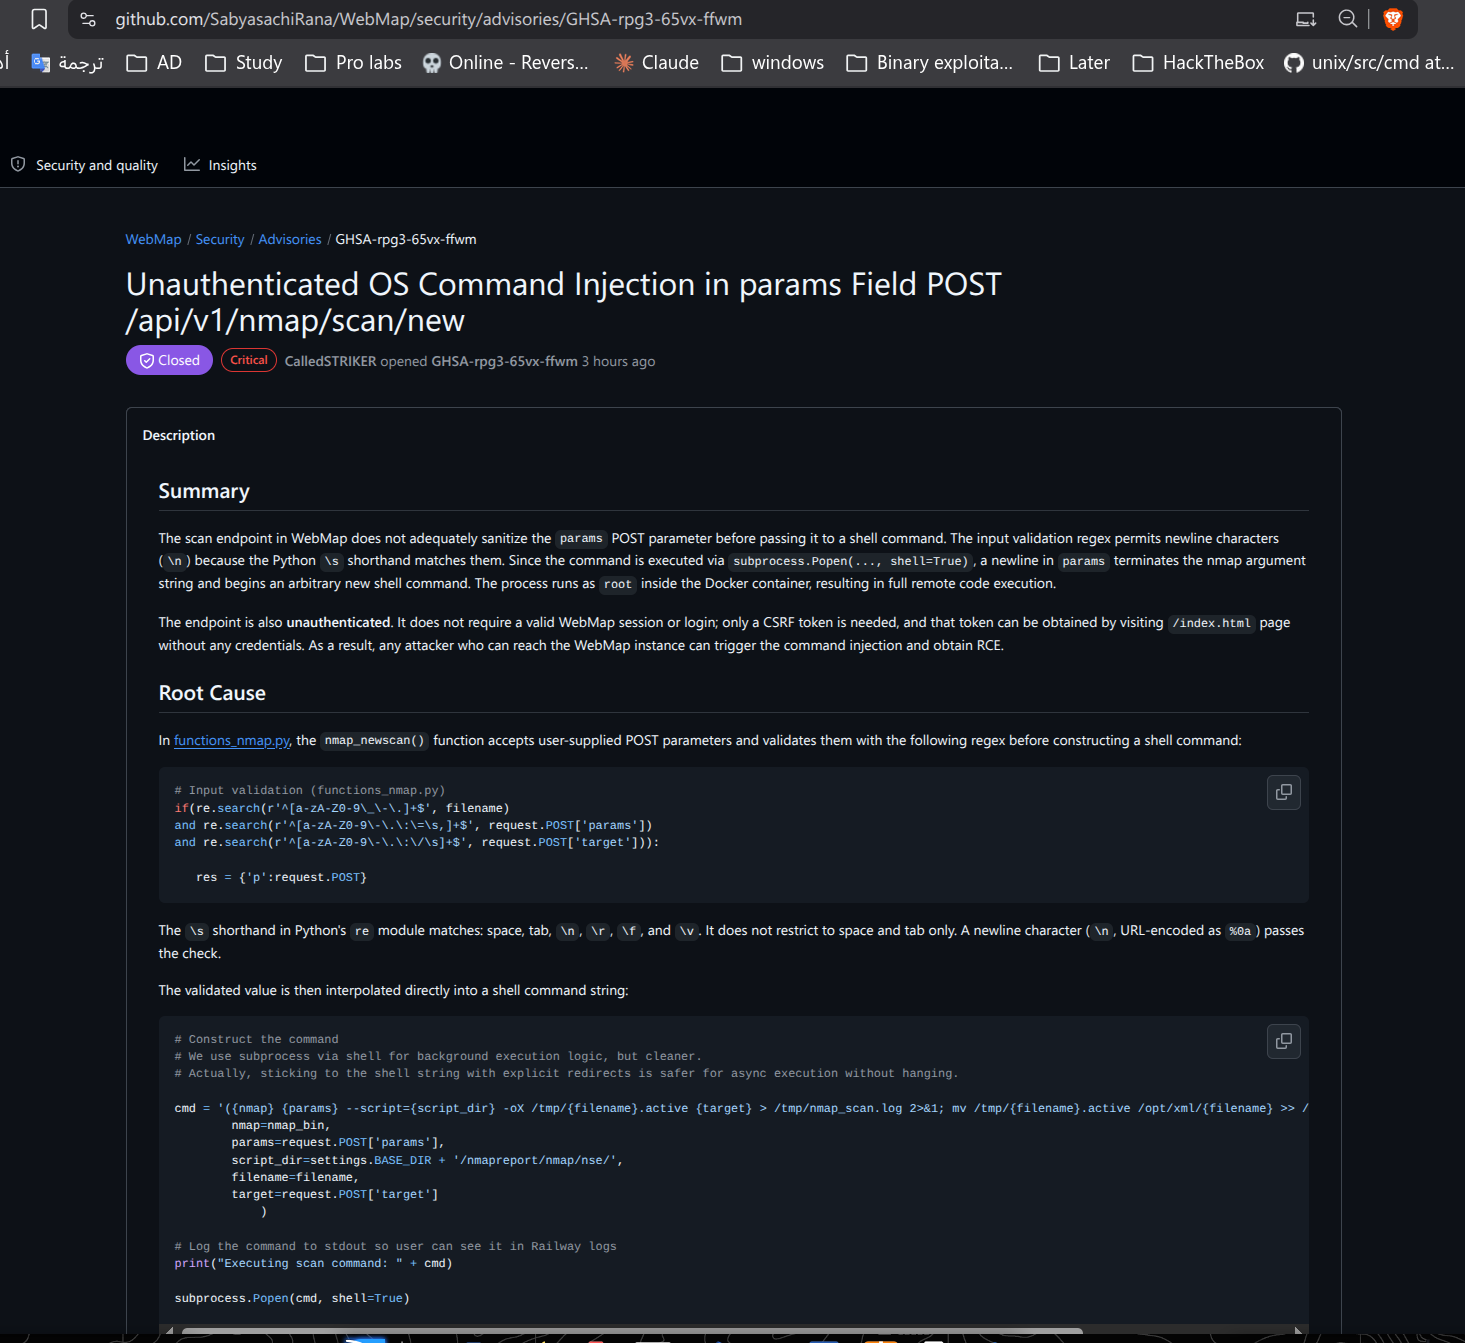
A security vulnerability has been detected in SabyasachiRana WebMap up to 8b95fe4dc301a3c09ddf145b895de0bf9f8d2a25. This affects the function nmap_newscan of the file functions_nmap.py of the component New Nmap Scan Handler. Such manipulation of the argument target/params leads to os command injection. The attack may be launched remotely. The exploit has been disclosed publicly and may be used. The name of the patch is 3d52f65803a2716bff14d938352c6fef45b0cfb6. A patch should be applied to remediate this issue. This issue got fixed with a silent patch.
Source: the CVE record as published by its numbering authority, via NVD and CVE.org.
The underlying weakness: Improper Neutralization of Special Elements used in a Command
The product constructs all or part of a command using externally-influenced input from an upstream component, but it does not neutralize or incorrectly neutralizes special elements that could modify the intended command when it is sent to a downstream component.
How developers prevent this class of flaw
- If at all possible, use library calls rather than external processes to recreate the desired functionality.
- If possible, ensure that all external commands called from the program are statically created.
- Run time: Run time policy enforcement may be used in an allowlist fashion to prevent use of any non-sanctioned commands.
More Improper Neutralization of Special Elements used in a Command vulnerabilities (CWE-77)
Timeline
- CVE record published.
- CISA published its SSVC assessment (exploitation: poc, automatable: yes, technical impact: partial).
- Record last changed materially (score, affected products, status or references).
References
Patches and release notes
Other references
Recent Improper Neutralization of Special Elements used in a Command vulnerabilities
- 9.1 Critical severity
- 7.4 High severity
- 9.1 Critical severity
- 9.1 Critical severity
- 9.1 Critical severity
- 9.9 Critical severity
Spotted an error? Tell us.